The Essential Eight is the Australian Signals Directorate's set of eight baseline mitigation strategies, rated against maturity levels zero to three. For a school without a security team, start with multi-factor authentication, patching, tested backups and restricted administrative privileges, then work through the remaining controls one maturity level at a time.
Most independent schools I speak with have one or two people running IT, or an outsourced partner, and a business manager who carries the risk on the board's behalf. The Essential Eight can look like a university-sized project. It is not. Used well, it is a short list that tells you what to fix first and how to explain progress in plain language.
This guide covers what the Essential Eight is, why it matters in a school, which controls give the most protection for the effort, what a realistic year looks like, how to report to the board, and how it connects to cyber insurance. It ends with a checklist you can act on this term.
Key Takeaways
- The Essential Eight is a recognised baseline from the Australian Signals Directorate (ASD), not a legal requirement for independent schools.
- Maturity Levels run from zero to three. For most schools, Maturity Level One across all eight is the sensible first target.
- Multi-factor authentication, patching, regular backups and restricting administrative privileges usually give a school the most protection for the effort.
- A realistic year is: assess, fix the priority four, close the remaining gaps, then review and report.
- Board reporting should be one page, in plain language, with decisions attached.
- Cyber insurance questionnaires ask about the same controls, so the work pays off twice.
Free, 45 minutes
Start with a school IT health check.
We look at your environment, rank the risks in plain English and tell you what deserves attention first. Built for schools, with nothing to prepare.
Summary Table
| Strategy | What it does for a school | Usual priority |
|---|---|---|
| Multi-factor authentication | Stops a stolen password being enough to get into email, Microsoft's cloud office suite or the student system | First |
| Patch operating systems and applications | Closes known flaws before they are used against you | First |
| Regular backups | Gives you a clean restore after ransomware, error or failure | First |
| Restrict administrative privileges | Limits how far one compromised account can reach | First |
| Application control | Allows only approved software to run | Later, needs tuning |
| Configure Microsoft Office macro settings | Blocks a common route for malicious documents | Later, usually quick |
| User application hardening | Reduces risk from browsers, PDF readers and similar tools | Later |
What is the Essential Eight and what do the maturity levels mean?
The Essential Eight is a set of eight mitigation strategies published by the Australian Signals Directorate (ASD) through the Australian Cyber Security Centre on cyber.gov.au. The Essential Eight Maturity Model rates how well each strategy is implemented, from Maturity Level Zero to Maturity Level Three, so you can set a target and measure progress.
The eight strategies are:
- Application control
- Patch applications
- Configure Microsoft Office macro settings
- User application hardening
- Restrict administrative privileges
- Patch operating systems
- Multi-factor authentication
- Regular backups
The maturity levels describe how capable an attacker a set of controls is designed to resist. As ASD describes the model, Maturity Level Zero means there are weaknesses in your overall security posture. Level One is partly aligned to the intent of each strategy and addresses attackers using widely available tools and common techniques. Level Two addresses attackers willing to invest a little more effort and skill. Level Three addresses more adaptive attackers who are less reliant on public tools.
Two practical points. First, ASD advises reaching the same maturity level across all eight before moving to a higher one, so do not polish one control to Level Three while another sits at zero. Second, ASD updates the model from time to time, so check the current version on cyber.gov.au before you set a target. Do not rely on a summary written two years ago, including this one.
Is the Essential Eight mandatory for independent schools?
No. Under the Commonwealth Protective Security Policy Framework, the Essential Eight is a requirement for non-corporate Commonwealth entities, not for independent schools. For schools it is a widely recognised baseline that boards, insurers and auditors increasingly use as a common language. That makes it a sensible target, not a legal obligation.
That does not mean schools have no obligations. Most independent schools are covered by the Privacy Act 1988 and the Notifiable Data Breaches scheme run by the Office of the Australian Information Commissioner (OAIC). If an eligible data breach is likely to cause serious harm, you may need to notify affected families and the OAIC. Your school association or sector body may also set expectations, so it is worth asking.
For figures on education sector breaches, go to the OAIC's Notifiable Data Breaches reports and use the latest edition. For wider threat context, our roundup of Australian cybersecurity statistics points to the primary sources.
Why does the Essential Eight matter in a school?
Schools hold sensitive records about children and families, take fee payments, run staff accounts that reach payroll and email, and operate on a term calendar that cannot pause. A cyber incident in a school is therefore an operational problem as much as a technical one. The Essential Eight targets the weaknesses that cause those incidents.
Consider what a typical independent school holds:
- Student and family records: contact details, custody arrangements, medical and wellbeing notes, and learning support information.
- Fee payments and banking details: invoices, direct debit information and bank change requests that a fraudster would love to imitate.
- Staff accounts: Microsoft 365 or Google logins that open email, files and often the student management system.
- A calendar that does not move: reports, exams, camps, parent-teacher interviews and enrolments all land on fixed dates.
That last point is the one I raise most with business managers. A business can sometimes close for a day. A school in the middle of Term Three assessments cannot. Our approach to education IT starts from the calendar, because that is where an outage hurts most. The broader work on cyber security sits on the same foundation.
I am not interested in selling fear here. Most schools I look at are doing many things reasonably well. The point of a baseline is to find the few gaps that matter and fix them in order.
Which of the Essential Eight should a school do first?
Start with multi-factor authentication, patching, regular backups and restricting administrative privileges. These address the most common ways attackers get in and the most common ways a school loses a week: stolen passwords, known software flaws, no clean restore, and accounts with too much power. They also suit a small team.
Note that patching covers two of the eight strategies, applications and operating systems, so this priority list touches five of the eight in practice.
Multi-factor authentication
Multi-factor authentication (MFA) means a password alone is not enough to log in. For schools, start with staff email and Microsoft 365, then administrator accounts, then remote access and any internet-facing systems. Students are a separate decision, covered in the FAQs. Rolling out multi-factor authentication for schools well is as much about staff communication as configuration. Plan for lost phones, casual and relief teachers, and the staff member who changed their number over the holidays.
Patching
Most attacks use flaws that already have a fix. The Maturity Model sets patching timeframes that depend on the maturity level and on whether an exploit exists, so read the current version for the exact requirements. In schools, the practical problem is rarely the patch itself. It is the old device: the classroom laptop on an unsupported operating system, the printer nobody has updated, the legacy server running one old application. If a device can no longer be patched, it needs a plan to be replaced or isolated.
Regular backups
School data backups are your recovery plan, so they must be tested. The model expects important data, software and configuration to be backed up, retained, protected from modification or deletion by ordinary accounts, and restored as part of disaster recovery exercises. Ask a simple question: if the student management system were encrypted tonight, how long to restore it, and who has actually tried? A backup nobody has restored is a hope, not a control.
Restricting administrative privileges
Administrator accounts are the keys to the building. Give them only to people who need them, keep them separate from everyday accounts, and do not use them for browsing or email. In small schools I often find long-serving staff, former contractors or software vendors holding more access than anyone remembers granting. A tidy-up here costs little and removes a lot of risk.
The other four
Application control, Office macro settings, user application hardening and the rest matter too. They usually take more tuning, particularly application control, where teachers install classroom apps and device fleets are mixed. Do them after the priority four, and do them carefully so they do not break the lesson.
What does realistic progress look like over a year?
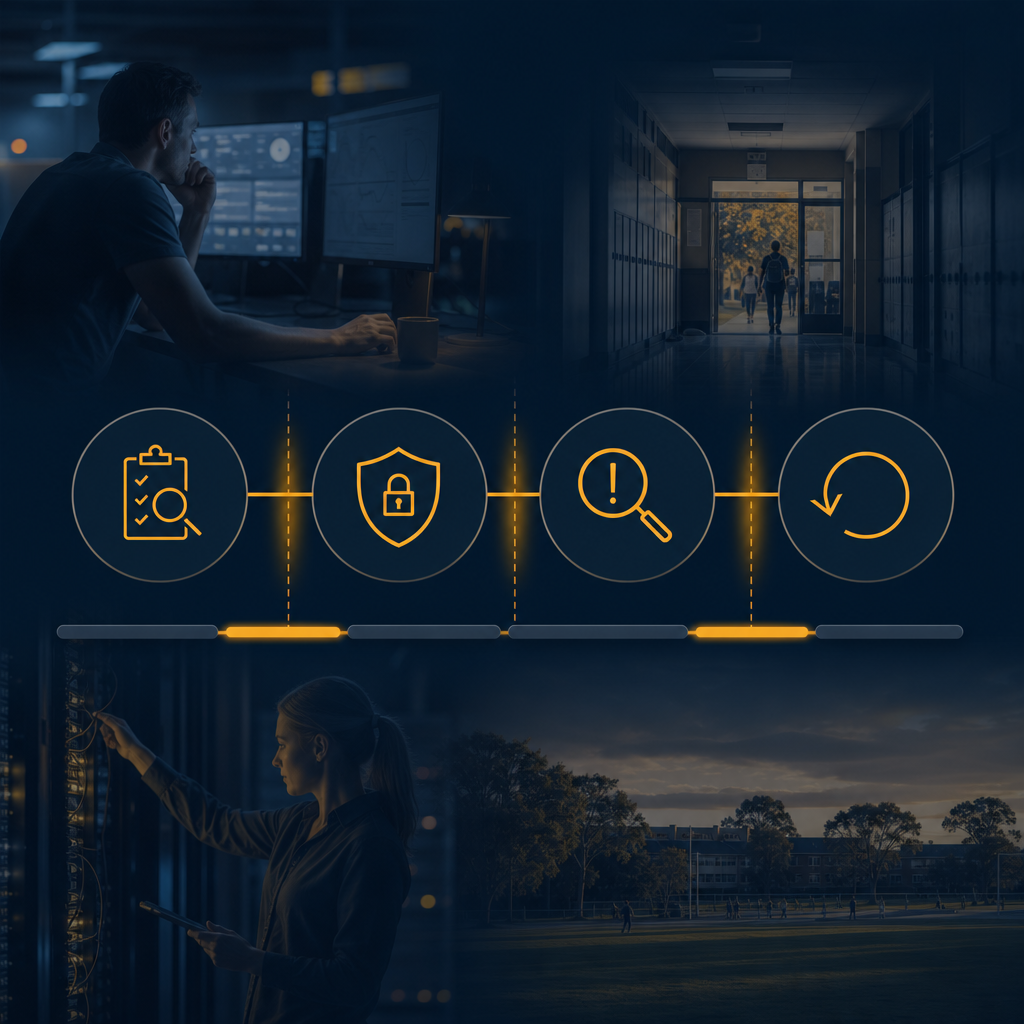
For a small school IT team or outsourced partner, a realistic year is: assess in Term One, fix the priority four through Terms Two and Three, close remaining gaps toward Maturity Level One across all eight, then review and report in Term Four. Level Two is usually a multi-year goal that depends on budget and risk appetite.
This follows the order we use for all security work: assess, protect, detect, recover. It is the whole job, in order. Your starting point will change the timing, so treat this as a shape, not a promise.
Term One: assess
Build an honest baseline. List devices and software, note which are unsupported, identify who holds administrator rights, find where backups live and when they were last restored, and see where MFA is and is not enforced. Rate each strategy against the current Maturity Model. Expect some uncomfortable findings. That is the point.
Term Two: protect the priority four
Roll out MFA to staff in stages. Clean up administrator accounts. Confirm backups are protected and run a real restore of a key system. Schedule disruptive changes for the school holidays or quiet weeks, never the week before reports.
Term Three: patch and retire
Set a regular patching rhythm and deal with devices that cannot be patched. This is where the device lifecycle matters. Devices are the easy part. The lifecycle is the work. A fleet that is planned, refreshed and retired on a schedule is far easier to keep patched. Begin the remaining controls, starting with Office macro settings.
Term Four: detect, review and report
Check that someone would notice if something went wrong, and that your incident contacts and recovery steps are written down. Reassess against the model, report to the board, and agree next year's target.
I have seen what this looks like when it is done as one end-to-end responsibility covering the network, cyber security and daily support at an independent school. The visible result was not a certificate. It was staff going back to teaching instead of troubleshooting. That is the outcome to aim for.
How do you report Essential Eight progress to the board?
Report on one page, in plain language: the current maturity level for each strategy, the target, what changed this term, what is next, and any risk the board is asked to accept. A simple traffic-light view tied to the model works well. Boards need decisions, not jargon.
A useful board paper includes:
- A scorecard: the eight strategies, current level, target level and a short note on each.
- Movement since last report: what improved and what has not moved, and why.
- Decisions needed: budget, device replacement, or acceptance of a known risk with a review date.
- Incidents and near misses: reported plainly, with what was learned.
- Dependencies: what relies on staff time, holiday windows or third parties.
If something is fine, say it is fine. Reports that raise every item as urgent teach the board to ignore them. Reports that rank risk in business terms let a board understand what it is buying and why.
How does the Essential Eight connect to cyber insurance questionnaires?
Cyber insurance proposal forms commonly ask about the same controls the Essential Eight covers: multi-factor authentication, backups, patching and privileged access. Insurer wording varies, so the Essential Eight does not guarantee cover or a particular premium. Doing the priority four makes the questionnaire easier to answer accurately.
Three habits help:
- Answer precisely. If a form asks whether MFA is enforced for all users and you have done staff but not students, say so. An inaccurate answer can cause problems at claim time.
- Keep evidence. Hold configuration screenshots, restore test records and your Essential Eight scorecard in one place.
- Ask your broker early. Raise the questionnaire before renewal, not the week it is due, so there is time to fix a gap.
Read the questions as a free checklist from people who see a lot of claims.
Why a school should resist chasing a perfect score
The contrarian view I hold is that the maturity score is a means, not the goal. A chart of eight bars invites a race to fill them in, and that can lead schools to roll out controls in a way that hurts teaching.
The better test is what I call the teacher test: if technology steals a minute of the lesson, it failed. MFA introduced badly on a Monday morning in Term Two will steal many minutes across a whole staff room. A patch that reboots a classroom computer mid-lesson will do the same. Good security should be built in by default and sequenced around the school day, so teachers barely notice it.
The second point is about people. Essential Eight progress that depends on one IT person's memory will not survive their holidays or resignation. Documented procedures, shared knowledge and a partner who owns the outcome, not just the ticket, matter as much as any control. We measure ourselves on your quiet weeks.
The third point is end of life. Old devices are among the hardest things to patch and the easiest to forget. When we retire client technology, we do it through PonyUp for Good: data is destroyed, devices are refurbished and resold, and half the profits are converted into meals. By SCCS's own figures, that partnership has funded more than 150,000 meals and diverted more than 40 tonnes of technology from landfill. For a school, the useful part is that retirement is planned, secure and documented, not a storeroom full of unwiped laptops.
A checklist for this term, and a calm first step
You do not need to do everything this term. Work through these in order and stop when you run out of time.
- Read the current Essential Eight Maturity Model on cyber.gov.au and agree a target (Maturity Level One across all eight is a sensible start).
- List every device and system, and mark anything that no longer receives updates.
- Check MFA coverage: staff email, Microsoft 365, administrator accounts and remote access.
- List every account with administrator rights and remove those that are not needed.
- Confirm where backups are stored and who can delete them.
- Restore one important system from backup and record how long it took.
- Agree a patching rhythm and who owns it.
- Put a one-page scorecard in front of the principal or board.
- Pull out your last cyber insurance questionnaire and compare the answers with reality.
If you would like a quick read on where you stand, the free ten-question Security Check takes about five minutes and is a good first step. If you would rather have someone look at the whole picture with you, book a free school IT health check. There is no pressure and no scare tactics. We will tell you what is fine, what needs attention, and in what order. For organisations that want to be safe, not scared, that is the right place to begin.
References
- Australian Signals Directorate, Australian Cyber Security Centre. Essential Eight: https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/essential-eight
- Australian Signals Directorate, Australian Cyber Security Centre. Essential Eight Maturity Model: https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/essential-eight/essential-eight-maturity-model
- Australian Government Attorney-General's Department. Protective Security Policy Framework: https://www.protectivesecurity.gov.au
- Office of the Australian Information Commissioner. Notifiable Data Breaches: https://www.oaic.gov.au/privacy/notifiable-data-breaches
Free download
The School IT & Cyber Readiness Checklist
Twelve points, ten minutes with a highlighter, and you know exactly what to fix first.
Frequently asked questions
Is the Essential Eight mandatory for independent schools?
No. Under the Commonwealth Protective Security Policy Framework, the Essential Eight is required of non-corporate Commonwealth entities. For independent schools it is a widely recognised baseline, not a legal requirement. Schools still have privacy and notifiable data breach obligations, and the Essential Eight is a practical way to meet them.
What Essential Eight maturity level should a school aim for?
Most schools should aim for Maturity Level One across all eight first, then decide on Level Two based on the information they hold, their risk appetite and their budget. ASD advises reaching a consistent level across all eight strategies before moving higher. The target is a board decision, informed by your IT team or partner.
Do we need multi-factor authentication for students as well as staff?
Staff and administrator accounts come first, because they hold the widest access. For students there is no single rule. Consider their age, the devices they use, and whether they log in from home. Many schools apply MFA for older students or for access from outside the school network. Decide this with your IT partner and record the reasoning.
How often should we test our school's backups?
The Maturity Model expects restoration to be tested as part of disaster recovery exercises. As a practical rule, test a real restore of a key system such as the student management system at least once a term, and again after any major change. Record the result and how long it took.
Can a school make progress without an in-house security team?
Yes. Most schools do. A small internal team or an outsourced partner can work through the priority four in order, report to the board each term and use the school holidays for disruptive changes. What matters is clear ownership, documented procedures and a regular review, not team size.
Ian Pearce
General Manager, Sales and Services at Southern Cross Computer Systems
Keep reading
IT solutions Australia
Comprehensive IT Solutions for Australian Businesses: Powering Growth and Efficiency
14 min read
network solutions Australia
Designing Robust Network Solutions for Australian Businesses: A Strategic Guide
16 min read
managed IT services pricing Australia
Understanding Managed IT Services Pricing in Australia: A Comprehensive Guide
12 min read