Choose a cyber security consultant by checking who will actually do and support the work, which frameworks they assess against (such as the ASD Essential Eight), what their certification covers, how they report findings and respond at 2am, and where your data goes. Then compare quotes on scope, not price.
Most Australian mid-sized organisations do not need more cyber security noise. They need a clear view of where they stand, a short ranked list of what to fix, and someone who stays to help fix it. This guide shows how to tell a useful cyber security partner from a provider selling a report.
You will get a plain description of what a good engagement delivers, the questions to ask before signing, the red flags worth walking away from, and a method for comparing quotes like for like. It is written for the IT manager, operations lead or finance lead who has to approve the spend without being a specialist. If you want the wider threat picture first, our Australian cyber security statistics page collects figures with their sources.
Key Takeaways
- A good engagement is a sequence: assess where you stand, agree a prioritised plan, get help implementing it, then monitor. A one-off report covers only the first step.
- Ask who does the work and whether those same people support you afterwards. Named people matter more than brand names.
- Ask which framework the assessment uses. The ASD Essential Eight is the natural Australian baseline for most organisations.
- A certificate such as ISO/IEC 27001 is only meaningful when you know its scope. Ask to see it.
- Fear-led selling, vague scope and tool-only answers are red flags. Calm, ranked, business-language advice is the standard to hold providers to.
- Compare quotes on scope, deliverables, people and response commitments before you look at the total.
Three minutes, no email needed
Where does your organisation actually stand?
Ten plain-English questions about the things that decide most breaches. Your result on screen straight away, and a free security audit if it turns up gaps.
Summary Table
| Area | What good looks like | What to be wary of |
|---|---|---|
| Engagement shape | Assessment, ranked plan, implementation help, ongoing monitoring | A single report with no follow-through |
| People | Named individuals who build and support | Anonymous teams, handover to a ticket queue |
| Reporting | Plain business language, ranked risks, clear owner | Technical dumps, everything marked critical |
| Framework | Assessed against a named, current framework such as the Essential Eight | A proprietary score nobody can explain |
| Certification | Certificate with a stated scope you can read | A logo with no scope behind it |
| Incident response | A named contact, written commitments, defined authority | Business-hours answers to a 2am question |
| Data handling | Clear answers on location, access, retention and deletion | Vague assurances |
| Selling style | Calm, specific, willing to say what is fine | Urgency, threats and countdown offers |
What a good cyber security engagement actually delivers
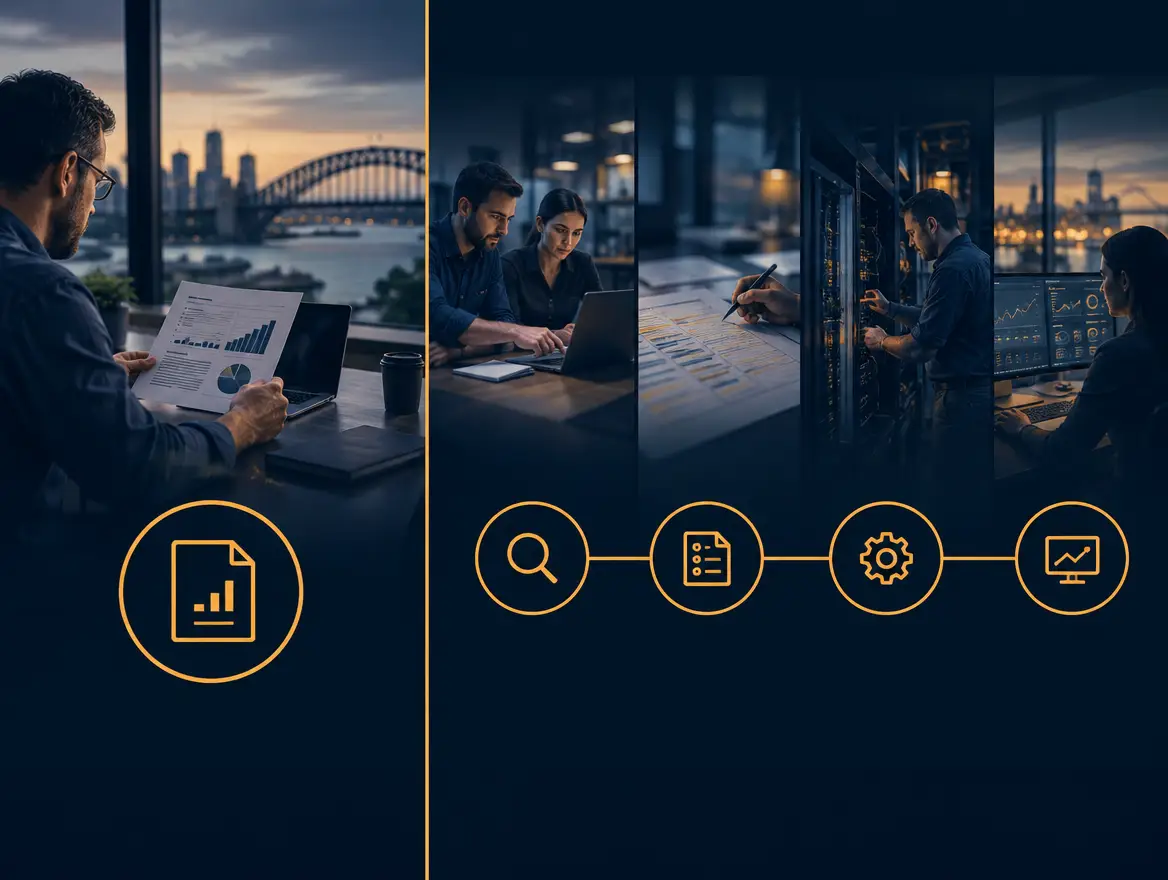
A good engagement delivers four things in order: an assessment of where you stand, a prioritised plan, help to carry the plan out, and ongoing monitoring. A one-off report delivers only the first. It tells you what is wrong, then leaves you holding a document and no one to act on it.
The assessment is the starting point, not the product. A useful cyber security assessment looks at your real environment: identities and multi-factor authentication, patching, backups, administrator access, email protection, devices and how people actually work. It should end with a ranked list, so a Board, Council or leadership team can see what is being bought and why.
The plan is where many engagements quietly fail. A report that lists forty gaps is not a plan. A plan puts the few that matter most first, says who owns each one, and fits your calendar and budget. Building blocks, not packages: you should be able to take the pieces you need without buying a bundle.
Then comes implementation and monitoring. Someone has to configure the controls, test the backups, watch for unusual activity and tell you when something needs attention. This is where managed services sit, and where the difference between a project contractor and a partner shows. Project contractors leave. Partners answer the phone.
The practical test is simple. Ask what you will have on the day the engagement ends, and what happens on the day after. If the answer to the second question is silence, you are buying a report.
Which questions should you ask before you sign?
Ask six questions before you sign: who does the work, how findings are reported, which framework is used, what the certification covers, who answers at 2am, and where your data goes. Written answers to these six separate a capable provider from one with a good brochure.
Who does the work, and will they be the people who support us?
Ask for the names and roles of the people who will carry out the assessment and the people who will support you afterwards. The best answer is that they are the same people. When the team that finds the problem is not the team that fixes it, knowledge gets lost at the handover and accountability goes with it.
Ask how long those people have been with the provider, and what happens if one of them leaves. Long-standing people who know your environment are worth more than a large bench of strangers. You want a partner who owns the outcome, not just the ticket.
How are findings reported, and to whom?
A report should be written for the person who has to make the decision. Ask to see a sample, with client details removed. Check that risks are ranked, explained in business terms and tied to a recommended action and an owner.
Also ask who receives the findings. Your executive team or Board should see a summary they can act on. Your technical staff should get the detail. If everything arrives as a single technical document, or everything is marked critical, the report is not helping you decide anything. A good provider will also tell you what is fine. If something is fine, say so.
Which framework do you assess against?
For most Australian organisations the sensible baseline is the Essential Eight, published by the Australian Signals Directorate through its Australian Cyber Security Centre (ACSC). It covers eight mitigation strategies: application control, patching applications, configuring Microsoft Office macro settings, user application hardening, restricting administrative privileges, patching operating systems, multi-factor authentication and regular backups. The accompanying Essential Eight Maturity Model describes maturity levels from zero to three.
Ask which edition of the maturity model the provider assesses against, because ASD updates it. Then ask them to explain, in plain words, why they would target a particular maturity level for you and not another. Other frameworks have their place, for example ISO/IEC 27001 for an information security management system, or IRAP assessments if you work with government. The point is that the provider names the yardstick, so you can compare results over time and against other quotes.
The Essential Eight is not a legal requirement for most private organisations. It is, however, increasingly what insurers, customers and tender documents ask about, so it is worth knowing where you stand.
Are you certified, and what does the certificate cover?
Certification to ISO/IEC 27001 shows that a provider runs an information security management system that has been independently audited. That is useful. It tells you how the provider protects its own operations and your information while working with you.
It does not tell you that your environment is secure, and it only covers what its scope statement says. Ask to see the certificate, the issuing certification body and the scope. Check that the scope includes the services you are buying, and that the standard version is current. ISO/IEC 27001:2022 is the current edition of the standard. If a provider is vague about scope, treat the badge as decoration.
What happens at 2am?
Incidents do not wait for business hours. Ask exactly what happens if you call at 2am on a Sunday. Who answers? Is it a named person or a queue? What can they do without waiting for your approval, such as isolating a device or disabling an account? What is committed in writing, and what is only a good intention?
Ask, too, how they help with your obligations afterwards. Under the Notifiable Data Breaches scheme administered by the Office of the Australian Information Commissioner (OAIC), an organisation that suspects an eligible data breach must carry out a reasonable and expeditious assessment, and the scheme sets a 30-day limit for completing it. A provider that has been through this before will talk about evidence, logs and decision-making, not only tools. Real people, not a ticket queue.
Where does our data go?
An assessment collects sensitive material: configurations, user lists, logs and sometimes copies of documents. Ask where that material is stored, who can access it, whether any support staff or subcontractors work offshore, how long it is kept and how it is deleted at the end. Ask the same questions about any monitoring tools that send data to a vendor's cloud.
The same discipline applies when equipment is retired. Old devices still hold data. Ask how the provider handles secure retirement, and whether you get evidence of destruction.
What are the red flags when choosing a provider?
The main red flags are fear-led selling, vague scope, no named people and tool-only answers. Any one of them is a reason to ask more questions. Two or more is usually a reason to walk away, because each signals that the provider is selling a product rather than owning an outcome.
Fear-led selling. Breach stories, countdown timers and warnings that you are about to be attacked are sales tactics. Risk is real, but it should be ranked and explained calmly. If a provider cannot tell you what is fine, they are not assessing, they are selling.
Vague scope. Phrases like 'full security review' mean little without a list of what is covered: which systems, which locations, which cloud services, which framework. Vague scope is how a quote looks cheap and then grows.
No named people. If you cannot find out who will do the work, you cannot judge their experience, and you cannot hold anyone accountable. Ask for names.
Tool-only answers. Ask how they would reduce your risk and the answer is a product name. A firewall from a vendor such as Fortinet is a good building block, but a tool is not a plan. Tools need configuring, monitoring and someone watching the alerts. Ask who does that, and how often it is reviewed.
A softer warning sign is a provider that never says no. If every question is answered with 'yes, we do that', ask for an example of something they would advise you not to buy.
How do you compare cyber security quotes like for like?
Compare quotes by lining up scope, deliverables, people, reporting, response commitments and exclusions side by side, then ignore the headline price until those match. Two quotes with the same total can cover very different work, and the cheaper-looking one often leaves out the part that matters after handover.
Build a simple grid and fill it in for each provider. If a quote does not answer a row, ask, and note whether the answer came in writing.
| Comparison row | What to check |
|---|---|
| Scope | Systems, sites, cloud services and user groups included and excluded |
| Framework | Named framework and edition, and the target level |
| Deliverables | Report, ranked plan, executive summary, technical detail |
| People | Named assessor, named support contact, continuity if they leave |
| Implementation | What is included, what is quoted separately |
| Monitoring | What is watched, by whom, how alerts are handled |
| Incident response | Contact method, hours, authority to act, written commitments |
| Data handling | Storage location, access, retention, deletion |
| Reviews | How often progress is reviewed and reported |
| Exclusions | What happens if the assessment finds something outside scope |
Two more habits help. First, ask each provider to say in one paragraph what you will be able to do or show at the end that you cannot today. If they cannot, the deliverable is unclear. Second, ask for a reference conversation with an organisation of similar size, and ask that organisation what happened after the report arrived.
If you are comparing a one-off assessor with a managed security provider in Australia, remember they are doing different jobs. Price the whole path to the outcome you want, not the first step alone.
How does SCCS approach cyber security?
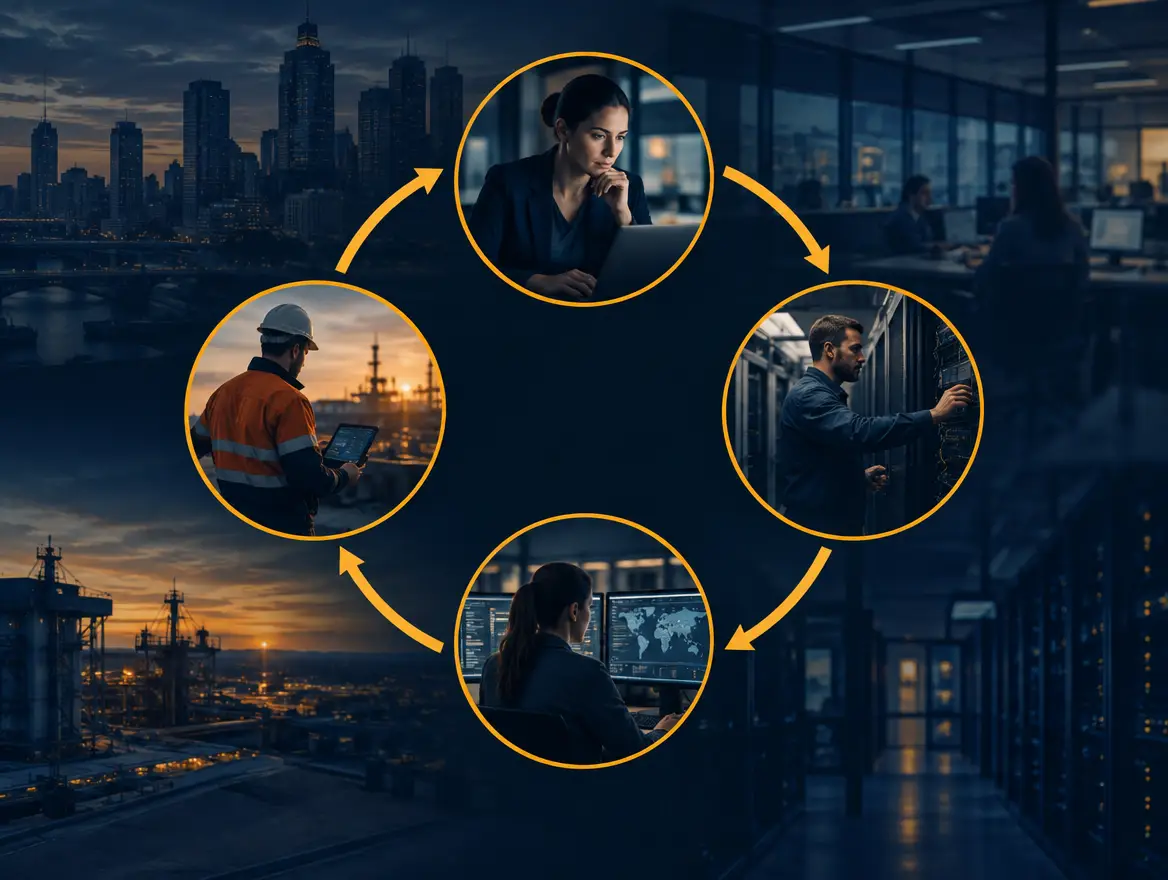
SCCS works through four disciplines in order: assess, protect, detect, recover. We call it the whole job, in order, and we review it on a regular rhythm. SCCS is certified to ISO/IEC 27001:2022 by Intertek (certificate 0223646), and we explain risk in business terms, never in fear.
In plain English, the four steps look like this.
- Assess. We look at where you stand today, against a named framework, and tell you what matters most and what is already fine.
- Protect. We put the controls in place that close the gaps that matter, such as access, patching, email protection and backups, in an order that suits your operation.
- Detect. We watch for unusual activity so problems are found early, while they are small.
- Recover. We make sure backups work and that there is a tested way back, so a bad day does not become a bad month.
The same people build and support the result, with a named lead and documented knowledge, so accountability does not change hands. It is the boring stuff, done brilliantly, forever. It is for organisations that want to be safe, not scared.
The teacher test: what a quiet week tells you
The best sign of a good security partner is a quiet week. If staff are not thinking about security, nothing urgent lands on your desk and the report says plainly what is fine, the work is succeeding. Be wary of any provider who cannot tell you what you do not need.
In my experience, buyers focus on the sales process and under-weight the quiet. Imagine two providers present to your leadership team. One shows a wall of red findings and a countdown. The other shows a short ranked list, says three areas are already sound and explains the first two actions in business terms. The second sounds less dramatic and is almost always the better partner. Drama is cheap to produce. Calm is built from experience.
At an independent school where SCCS took responsibility for the network, cyber security and daily support, the outcome we cared about was simple: staff could go back to teaching instead of troubleshooting. We call it the teacher test. If technology steals a minute of the lesson, it failed. The same test applies in an office, a warehouse or a finance team. Does security help people get on with their work, or does it get in the way?
On a government data centre and continuity project, the measure was different but related: the team gained resilience its auditors could sign off. That is a good standard for any buyer. Ask whether the work would survive an auditor reading it, not whether it would impress a salesperson.
We measure ourselves on your quiet weeks. Ask any provider you are considering how they would measure themselves, and listen for whether the answer is about your outcomes or their activity.
A calm first step
You do not need to commission a full engagement to find out where you stand. The free three-minute Security Check asks a short set of questions and gives you a first view. If it turns up gaps, we offer a free security audit, so you can see the detail before deciding anything. There is no pressure and no countdown. If something is fine, we will say so.
References
- Australian Signals Directorate (ACSC), Essential Eight
- International Organization for Standardization, ISO/IEC 27001:2022 Information security management systems
- Office of the Australian Information Commissioner, Notifiable Data Breaches scheme
- Australian Signals Directorate (ACSC), Infosec Registered Assessors Program (IRAP)
Free download
The School IT & Cyber Readiness Checklist
Twelve points, ten minutes with a highlighter, and you know exactly what to fix first.
Frequently asked questions
How much does a cyber security consultant cost in Australia?
Cost depends on scope, not on the consultant's brand. The main drivers are the size of your environment, the number of sites and systems, the framework used, and whether implementation and monitoring are included. Ask each provider for a written scope, and compare quotes row by row.
What is the difference between a cyber security consultant and a managed security provider?
A consultant typically assesses and advises, and the engagement ends with a report or plan. A managed security provider also implements, monitors and supports on an ongoing basis. Many organisations need both, ideally from the same people, so that the advice and the day-to-day work stay connected.
Do I need a provider that is certified to ISO/IEC 27001?
It is not essential, but it is a useful signal. It shows the provider's own information security management system has been independently audited. Ask to see the certificate and read the scope, because it only covers what it says it covers. It does not guarantee your own environment is secure.
What should a cyber security assessment report include?
A useful report names the framework and edition it assessed against, defines scope, ranks risks in business terms, recommends specific actions with owners, and says clearly what is already working. It should include a short summary for executives or a Board and the technical detail for your IT team.
Is the Essential Eight mandatory for private organisations?
For most private organisations it is not a legal requirement. It is the Australian Government's recommended baseline, published by ASD's Australian Cyber Security Centre, and insurers, customers and tender documents increasingly ask about it. It is a sensible yardstick even where nobody has asked yet.
Ian Pearce
General Manager, Sales and Services at Southern Cross Computer Systems
Keep reading
Australian cybersecurity statistics
Australian Cybersecurity Statistics 2026: Key Trends and Benchmarks
14 min read
Essential Eight for schools
The Essential Eight for Independent Schools: Where to Start
16 min read
IT solutions Australia
Comprehensive IT Solutions for Australian Businesses: Powering Growth and Efficiency
14 min read